AI Infostealer Malware: How Volta-Autodoxer Profiles Victims
AI infostealer malware may profile victims using stolen data. See what Volta-Autodoxer reportedly does, what remains unconfirmed, and how to protect accounts.
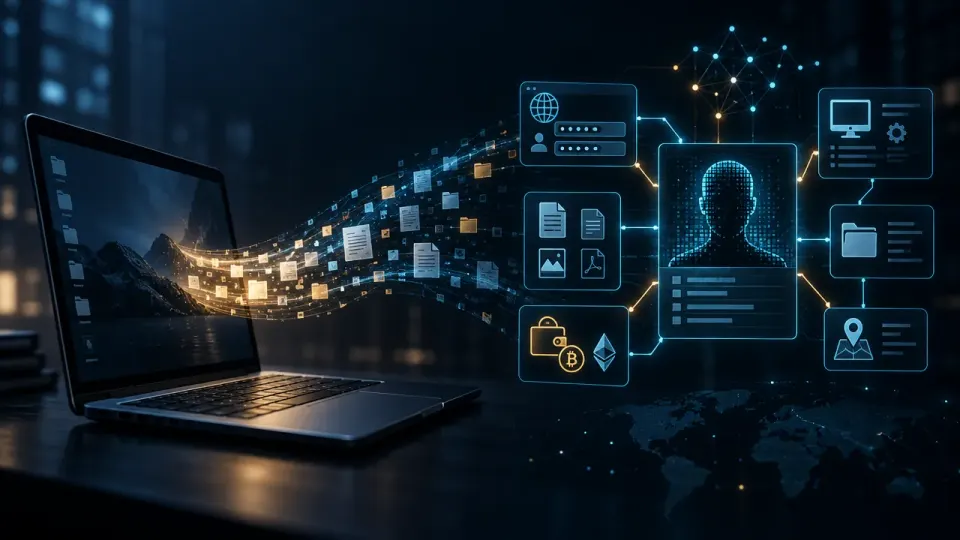
Table of Contents
Quick Answer
Volta-Autodoxer is a reportedly identified infostealer that uses AI to analyze stolen data and guide further searches for information that could profile a victim. Researchers have not confirmed its use in attacks, real-world victims, or the scale of any incidents.
What Researchers Reported About Volta-Autodoxer
The malware’s initial collection reportedly targets a broad range of information from infected devices and accounts. That includes browser passwords, Microsoft OAuth tokens, cookies, payment-card details and cryptocurrency wallet seed phrases. It also seeks active sessions for services such as Discord, Telegram, Steam and Roblox.
These targets are not unique to AI-powered malware. Infostealers have long been designed to take credentials, authentication material and other sensitive data. The distinguishing feature in Volta-Autodoxer’s reported design is what happens after that first collection: the malware uses its findings to guide further searches.
How the Malware Uses Stolen Data to Build a Victim Profile
According to the report, a second sweep can use information from the initial theft to search central accounts such as Gmail. Email accounts may contain details that are valuable beyond the messages themselves, including receipts, order histories and clues about a person’s location and routines.
By connecting these details, the malware reportedly attempts to “autodox” a victim - assemble a more complete picture of their identity, habits and circumstances. For example, an order confirmation might reveal a purchase and delivery location, while other messages could provide context about the victim’s accounts or activities. The value lies in linking scattered information, rather than simply collecting a larger number of passwords.
That kind of profiling could help an attacker decide which stolen information deserves attention or support follow-on targeting. However, the report describes capabilities attributed to the malware, not proof that a particular victim was profiled or that the information was used in a subsequent attack.
What AI Adds - and What the Report Does Not Confirm
Volta-Autodoxer illustrates how commercial large language models (LLMs) may be used to augment existing cybercrime tools. In this case, AI is reportedly involved in analyzing collected data and guiding searches. The core theft - harvesting passwords, tokens, cookies and account sessions - remains conventional infostealer activity. AI does not replace those techniques; it may help interpret what they uncover.
Cisco Talos reportedly used its CAIRN framework to flag tools incorporating AI capabilities. The framework’s use reflects a broader effort to identify malware that applies AI as part of its operation, rather than treating every familiar credential-stealing function as an AI feature.
There is an important limit to what is known: Talos did not track whether Volta had been used in attacks. The report therefore does not establish real-world deployment, confirmed victims or the scale of any incidents. Its described capabilities should not be read as evidence that the malware has successfully profiled people in active campaigns.
The practical takeaway is still straightforward. Infostealers can expose more than saved passwords: stolen cookies and tokens may provide access to existing sessions, while email and purchase records can reveal personal details. Use unique passwords, enable multifactor authentication, and revoke sessions or tokens you do not recognize. Review account activity and treat unexpected sign-in alerts as a reason to secure the affected account promptly.
Step-by-Step Guide
Use unique passwords
Create a different strong password for each account, preferably with a password manager, so one stolen credential cannot unlock multiple services.
Enable multifactor authentication
Turn on multifactor authentication for email, financial, gaming, and messaging accounts to add a verification step beyond the password.
Review account activity
Check sign-in history and security alerts for unfamiliar devices, locations, or activity, and investigate unexpected notifications promptly.
Revoke unfamiliar sessions and tokens
Sign out unknown devices and remove unrecognized connected apps or access tokens, then change the affected account password.
Key Statistics
- The report names five types of initially targeted information: browser passwords, Microsoft OAuth tokens, cookies, payment-card details, and cryptocurrency wallet seed phrases.This count is based on the data types attributed to Volta-Autodoxer in the article; it describes reported capabilities, not confirmed theft from victims.
- Four services are named as targets for active sessions: Discord, Telegram, Steam, and Roblox.The article lists these examples among the sessions the malware reportedly seeks; the report does not confirm successful access to accounts on these services.
- The report does not establish confirmed victims, real-world attack deployment, or incident scale.According to the article, Cisco Talos did not track whether Volta had been used in attacks, so the reported capabilities should not be treated as evidence of active campaigns.
Frequently Asked Questions
What is Volta-Autodoxer?
How does AI infostealer malware profile victims?
What information can an infostealer take?
How can I protect my accounts from infostealer malware?
Key Takeaways
- Volta-Autodoxer reportedly collects credentials, tokens, cookies, payment-card details, wallet seed phrases, and active service sessions.
- Its reported AI-assisted analysis may guide follow-up searches, including searches of central email accounts such as Gmail.
- Email receipts and order histories can reveal details about a victim's purchases, location, routines, and accounts.
- The report describes attributed capabilities, but does not confirm deployments, victims, or successful profiling in active attacks.
- Use unique passwords and multifactor authentication, review account activity, and revoke unfamiliar sessions or tokens.