Gemini Refusals: How to Rephrase Harmless Requests
Learn why Gemini refuses harmless requests and how to rephrase prompts with clear scope, limited permissions, and approval checkpoints.
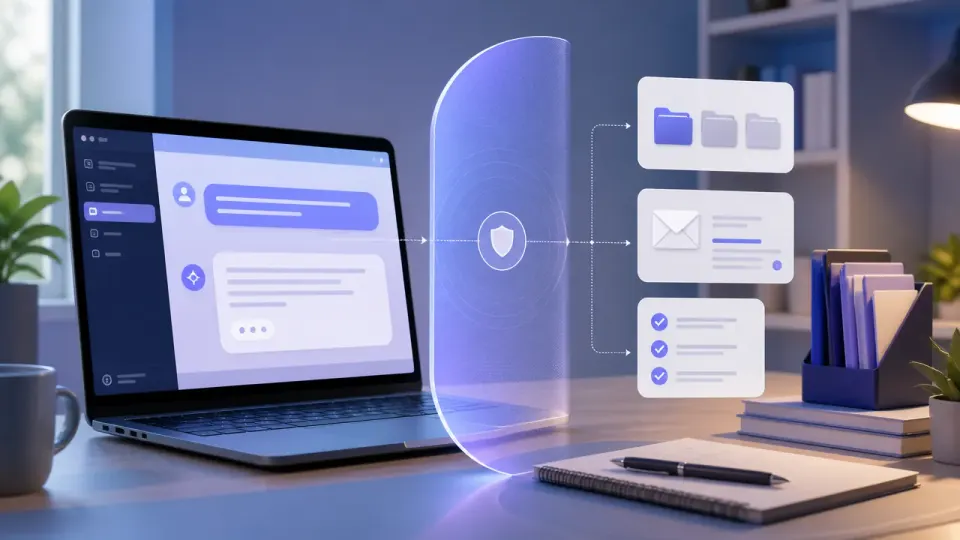
Table of Contents
Quick Answer
Gemini may refuse harmless requests when the instruction is ambiguous, involves sensitive data, lacks permissions, or could trigger external or irreversible actions. Rephrase the request by defining the goal, permitted inputs, output format, restrictions, confirmation requirements, and conditions for stopping.
That matters more as AI assistants become more agentic. Gemini may be able to work with business data, applications, files, email, calendars, and other services. A request that once produced only text could now lead to changes in a document, a message, or a workflow. A refusal is therefore often a signal that your request needs a clearer goal, narrower scope, or explicit permission boundary - not necessarily that Gemini considers the task harmful.
A harmless request can still look risky to Gemini
Consider the instruction: “Clean up my project files and notify the team.” Your intention may be routine organization. But the request leaves several questions unanswered:
- Which files count as project files?
- May Gemini rename, move, or delete them?
- Which team members should be notified?
- Should it send a message or prepare a draft?
- What happens if a file contains confidential information?
The broader the instruction, the more possible consequences it has. Gemini may respond cautiously when it cannot distinguish analysis from execution, or when the request could involve data and systems you are not authorized to use.
The main reasons Gemini refuses a legitimate request
State the exact outcome you want. “Compare the totals in these two spreadsheets and list discrepancies” is safer and easier to interpret than “Audit the finance folder.”
Connected apps increase this complexity. Access to Drive, Gmail, Calendar, customer systems, or internal databases should be limited to the data needed for the task. Gemini Enterprise permissions and administrator policies may also prevent an action that your account appears able to request.
Ask for analysis or a draft first. Make execution conditional on your confirmation.
Use a least-privilege prompt to clarify what Gemini may do
A useful prompt gives Gemini only the authority needed for the immediate task. Include these seven parts:
A reusable structure looks like this:
Act as a project analyst. Compare the figures in the two attached spreadsheets for April and May. Use only those files. Return a table of differences and a three-sentence summary. Do not edit, share, or delete anything. If a value is unclear, identify it rather than guessing. Ask for confirmation before taking any external action.
This approach clarifies legitimate intent while reducing unnecessary permissions.
Before-and-after examples for common Gemini refusals
Clearer: “Summarize the three documents I attached about the acquisition. Include the proposed timeline, open risks, and named owners. Do not search other Drive files or reveal personal contact details. If the documents conflict, show both statements.”
The revised request names the permitted source and prevents an unnecessarily broad search.
Clearer: “Draft an email to the client using the delay details in the attached project note. Keep the tone professional and do not add causes that are not in the note. Do not send the email, access other contacts, or modify the calendar. Wait for my approval after showing the draft.”
The key distinction is between drafting and sending. State it explicitly.
Clearer: “First, identify overdue invoices in the connected billing report and return invoice number, customer, amount, and due date. Do not contact anyone or change records. After I review the list, draft separate customer messages for my approval. Only update records after I give explicit confirmation.”
Staging the work limits the impact of an error and creates checkpoints before external actions.
What to do when Gemini still refuses
First, remove details that are not necessary. Replace full personal information with labels, attach only the relevant excerpt, and avoid including credentials, private identifiers, or unrelated records.
Next, split the task into smaller steps. Ask Gemini to summarize the supplied data before asking it to produce recommendations. Request a draft before requesting delivery. If the issue is permissions, ask what source or action is unavailable rather than repeatedly issuing the same instruction.
You can also ask:
Which part of this request is blocked - the data source, the requested action, the sensitivity of the information, or the scope? Please suggest a safe alternative that produces an analysis or draft without making changes.
If Gemini identifies a policy or administrator restriction, do not try to disguise the request. Ask the relevant administrator to review access, or complete the restricted step yourself through an approved process.
Rephrase for clarity, not to bypass safety controls
Gemini is not unique in applying usage and safety boundaries. Other assistants, including Anthropic's Claude, also restrict misuse and harmful interactions. Rephrasing should make a legitimate task more precise and reduce unnecessary access - not conceal intent or evade a safeguard.
Try the least-privilege format on your next request: state the exact goal, name the permitted source, request analysis or a draft first, prohibit unwanted actions, and require confirmation before anything external or irreversible happens. A clearer prompt gives Gemini a safer path to complete useful work.
Step-by-Step Guide
Define one specific objective
State the exact result you want, such as comparing two spreadsheets or drafting one email, instead of using broad phrases like 'handle everything.'
Name the permitted inputs
Identify the exact files, folders, applications, or pasted text Gemini may use, and exclude unrelated sources.
Separate analysis from execution
Ask Gemini to summarize, compare, or prepare a draft first rather than immediately sending messages, editing documents, or changing records.
Set explicit restrictions
State what Gemini must not do, including searching other files, exposing personal details, deleting content, sharing information, or modifying systems.
Require confirmation and stop conditions
Tell Gemini to pause before external or irreversible actions, ask questions when information is unclear, and report missing access instead of guessing.
Key Statistics
- A least-privilege Gemini prompt can be structured around 7 control elements.This article identifies seven elements: role, objective, permitted inputs, requested output, constraints, confirmation requirements, and stop conditions.
- The article presents 3 common risk categories behind seemingly harmless refusals.The categories are ambiguous instructions, sensitive data or missing permissions, and requests that could trigger external or irreversible actions.
- The article includes 3 staged workflow checkpoints for higher-risk tasks.Its invoice example separates identification, message drafting, and record updates so the user can review each stage before execution.
Frequently Asked Questions
Why does Gemini refuse harmless requests?
How can I rephrase a Gemini prompt that was refused?
Can Gemini access my connected apps and business data?
How do I stop Gemini from taking unwanted actions?
Key Takeaways
- Broad instructions can hide unclear scope, sensitive data exposure, or unauthorized actions.
- Connected apps and external actions require tighter permissions than text-only analysis.
- Use a least-privilege prompt that names the goal, sources, output, limits, and stop conditions.
- Ask Gemini to analyze or draft before allowing it to send, edit, delete, or update anything.
- Rephrasing should clarify legitimate intent, not conceal it or bypass safety and administrator controls.