Persistent Gemini Agents Get Their Own Workspace Accounts
Persistent Gemini agents could get Gmail, Calendar, and Drive identities, changing enterprise AI governance and enabling accountable digital coworkers.
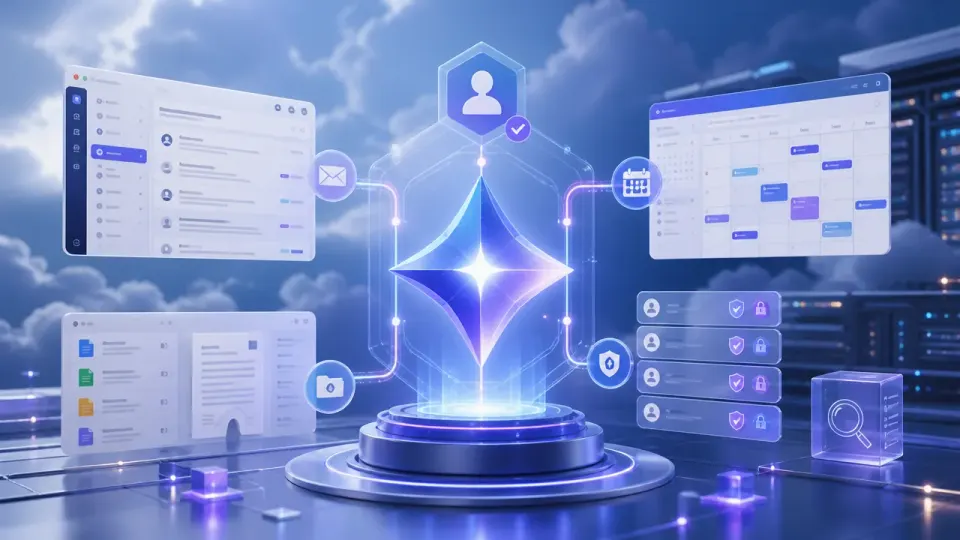
Table of Contents
Quick Answer
Persistent Gemini agents are designed to pursue business objectives over time, using tools, systems, and stored context beyond a single prompt. Google Cloud's proposed Workspace identity could give them dedicated Gmail, Calendar, and Drive accounts, making their actions more visible and governable.
Google has not said whether this Workspace footprint will be available to every Gemini agent or only to agents configured as persistent coworkers. It also has not clarified the licensing and provisioning model. Still, the change points to a broader shift in enterprise AI: agents are becoming ongoing participants in business workflows rather than disposable interfaces for individual tasks.
What persistent Gemini agents are and why Workspace identity matters
A conventional AI assistant typically receives an instruction, produces an answer or completes an action, and stops. Persistent Gemini agents are designed to pursue objectives over time. They can plan work, use custom skills and tools, connect to internal business systems, and continue operating as circumstances change.
Giving an agent its own organizational identity provides a clear home for that activity. Instead of sending a message or creating a file under an employee's account, the agent could use its own Gmail address, Calendar presence, and Drive storage. Employees could then recognize whether a task came from a person or an AI coworker and find the agent's work in a dedicated Workspace footprint.
For example, a project agent might monitor an approved inbox, organize project documents in Drive, schedule recurring meetings, and coordinate follow-up tasks. Its continuing identity could preserve context across those activities instead of requiring an employee to restate the objective each time.
How an AI coworker can use Workspace and business systems
Google describes persistent agents as accessible through several entry points, including tagging, email, shared resources, and group chats. Their experience is intended to span Google Workspace and Microsoft 365, as well as platforms such as Slack and ServiceNow. Users may also interact with them across iOS, Android, Windows, Mac, and the command line.
That range matters because enterprise work rarely stays inside one application. An agent might receive a request in a group chat, review approved material in Drive, check availability in Calendar, send a status update through Gmail, and write information to an internal business system.
The Workspace account does not automatically make those actions safe or unlimited. Administrators will need to define which mailboxes, calendars, files, tools, and business systems an agent can access. A scheduling agent may need permission to view calendars but not read message content. A recruiting agent may need access to a controlled Drive folder without permission to share files externally.
The governance shift: identity, permissions, and audit trails
A persistent AI coworker creates a different governance problem from a one-time task agent. A temporary agent may act within a narrow session and disappear when the task ends. A persistent agent has continuing identity, stored context, permissions, and potentially broader authority. Those features make it more useful, but also increase the consequences of misconfiguration or unauthorized access.
Google says actions can generate an audit trail attributed to the agent rather than to an individual employee. That distinction is important for investigations and accountability. An administrator reviewing a file change, calendar event, or email should be able to determine that an agent performed the action, identify the agent's owner and permissions, and understand what triggered the work.
Organizations will also need controls for approval thresholds, data retention, external sharing, credential rotation, human escalation, and shutdown. A useful policy might allow an agent to draft customer emails but require employee approval before sending them, or permit calendar bookings only within predefined hours and meeting types.
What enterprise administrators still need to clarify
Several operational questions remain open. Administrators need to know whether Gmail, Calendar, and Drive can be enabled or disabled independently, how coworker accounts are provisioned, and whether each account requires an additional Workspace license. They also need details on ownership, storage limits, delegated access, retention policies, and offboarding when an agent is retired.
The answers will determine whether persistent Gemini agents can fit existing identity and access management programs. Before deployment, organizations should define approved permissions, data access rules, identity and licensing requirements, and audit policies for long-running agents.
The central idea is clear: persistent Gemini agents are being positioned as accountable digital coworkers with a place inside the organization. Their value will depend not only on what they can do, but on whether enterprises can see, limit, and review everything they do.
Step-by-Step Guide
Define the agent's business objective
Specify the long-running outcome, supported workflows, escalation rules, and conditions that determine when the agent should act or stop.
Provision a dedicated identity
Confirm whether the agent receives its own Workspace account, email address, calendar, and Drive storage, then document ownership and licensing requirements.
Scope permissions and data access
Grant only the mailboxes, calendars, files, tools, and business systems required for the defined workflow, with external sharing disabled by default.
Set approval and escalation controls
Require human approval for high-impact actions such as sending customer emails, changing sensitive records, or booking restricted meetings.
Monitor activity and retire safely
Review agent-attributed audit logs, rotate credentials, enforce retention policies, and define shutdown and offboarding procedures before launch.
Key Statistics
- Google Cloud's proposed agent identity spans three core Workspace services: Gmail, Calendar, and Drive.This count is derived from the article's description of the Workspace footprint attributed to Google Cloud's persistent Gemini agent announcement.
- The article identifies four major enterprise collaboration and business ecosystems for agent access: Google Workspace, Microsoft 365, Slack, and ServiceNow.These platforms are named in the article's summary of the entry points and systems that persistent agents are intended to work across.
- Persistent agents are described as operating across five listed environments or interfaces: iOS, Android, Windows, Mac, and the command line.The platform count comes from the article's account of Google Cloud's stated access and interaction environments.
Frequently Asked Questions
What are persistent Gemini agents?
Will Gemini agents get their own Gmail, Calendar, and Drive accounts?
Why does Workspace identity matter for AI agents?
How should enterprises govern persistent Gemini agents?
Key Takeaways
- Persistent Gemini agents are intended to operate continuously on long-running business objectives.
- Dedicated Gmail, Calendar, and Drive accounts could give AI agents an identifiable organizational presence.
- Workspace identity does not replace the need for carefully scoped permissions and administrator controls.
- Agent-specific audit trails could help enterprises distinguish AI actions from employee actions during investigations.
- Organizations still need clarity on licensing, provisioning, retention, ownership, and agent offboarding before deployment.